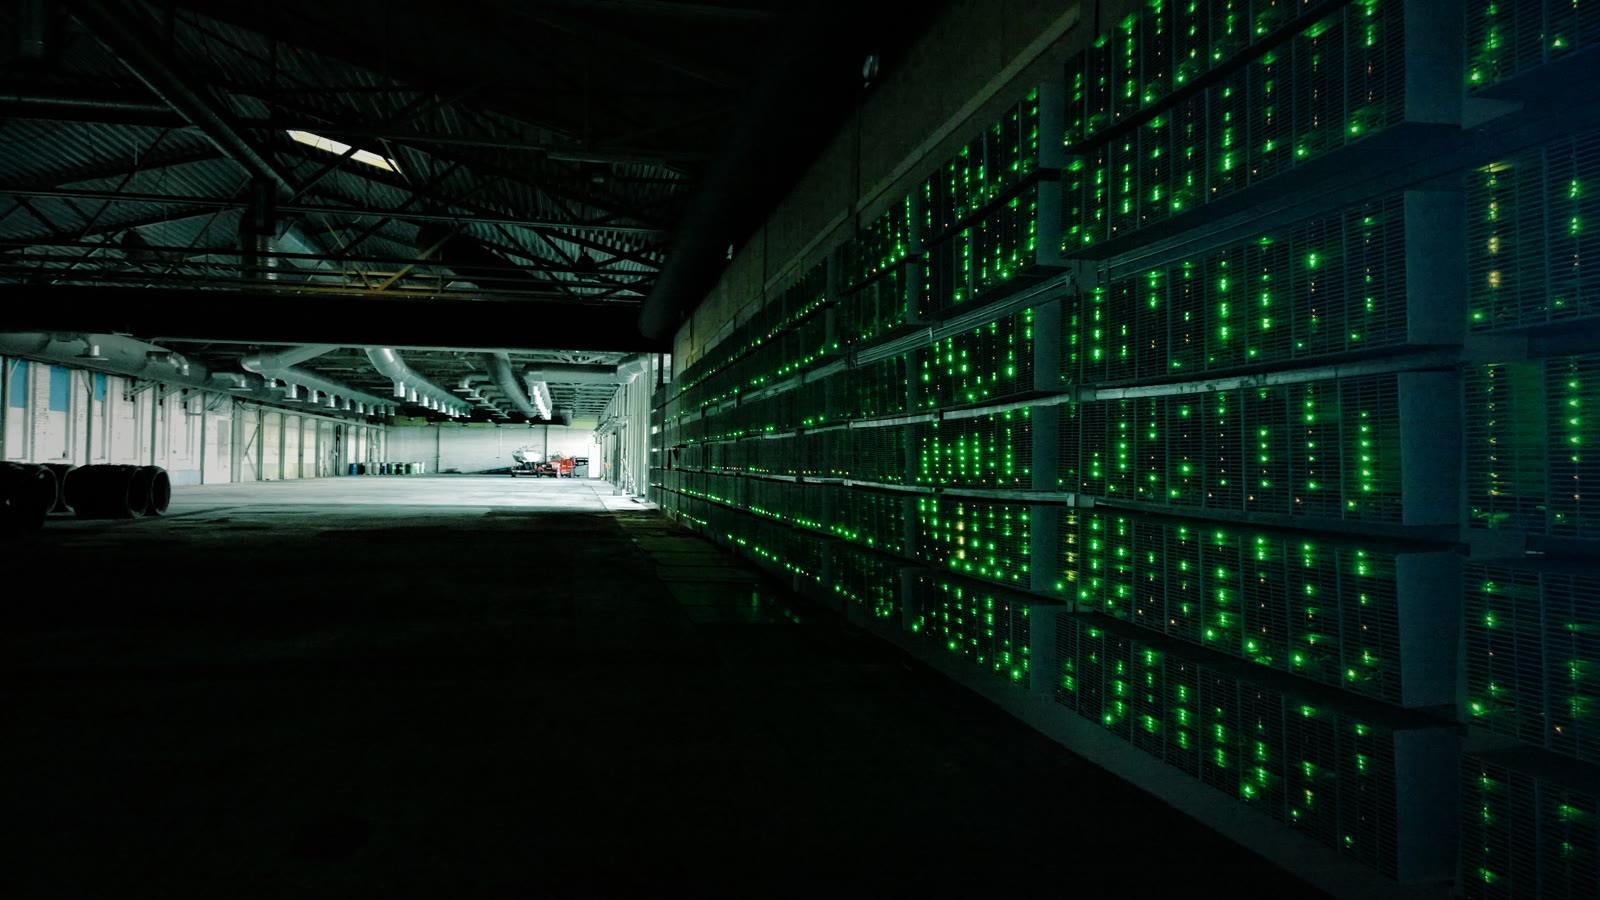
Proof of Work and Proof of Stake are often compared as two ways to “pick the next block.” That framing is too shallow. The deeper difference is the resource each system makes expensive to capture and the type of loss an attacker must absorb when trying to rewrite history. Proof of Work ties security to a continuing stream of external resources: specialized hardware, electricity, facilities, logistics and time. Proof of Stake ties influence to capital committed inside the protocol: validator stake, voting rules, penalties and, for provable conflicting behavior, the possibility that some of that stake is destroyed. Both approaches try to turn a software attack into an economic problem, but they do it with very different cost structures.
The most misleading shorthand is that PoW is “secured by electricity” while PoS is “secured by money.” Electricity without suitable hardware does not create useful hashrate. Tokens sitting passively in a wallet do not automatically give an attacker control over a validator set or finalized history. The entire path from a scarce resource to consensus influence matters: who proposes blocks, who validates them, which fork-choice rule selects canonical history, what the protocol calls finality, and which forms of conflicting behavior create an enforceable loss.
Proof of Work: why hashing becomes an economic barrier
In Bitcoin, miners receive or construct a block template, form a block header, and search for a header hash below the current target. Verifying the result is cheap; finding it in advance requires repeated computation. This asymmetry is the central engineering trick of PoW. Every validating node does not need to reproduce the miner’s entire search process. It only needs to verify that the submitted block and proof satisfy the rules.
“Work” is not an abstract mathematical quantity in an industrial network. It becomes ASICs, electricity contracts, transformers, cooling, buildings, network connectivity, maintenance, financing and the risk that hardware becomes obsolete. That is why the real cost of attacking a PoW chain cannot be inferred from the BTC price or network hashrate alone. It depends on how much comparable hardware can be acquired, how quickly power can be sourced, how long the operation must continue, how visible it becomes and what value remains in the equipment afterward.
Why the “51% attack” is useful shorthand but not a universal formula
The 51% phrase became popular because, in a simplified model, an attacker with a persistent majority of total hash power can on average extend an alternative chain faster than the honest network. But that does not mean 49% is always harmless or that 51% grants total control. Smaller shares can still increase the probability of short reorganizations and can matter in strategic mining behavior under certain network conditions. A majority of hashrate also does not let an attacker forge someone else’s signature, create arbitrary coins outside consensus rules, or force full nodes to accept an invalid state transition.
It is better to say that relative resource share changes the probability and persistence of control over ordering. Reversing one recent payment is a different problem from censoring a class of transactions for weeks. Changing protocol validity rules against the wishes of validating nodes is another problem again. The resource threshold must always be tied to a specific attack goal.
A simplified model of PoW attack economics
A rough operating-cost model can be written as C ≈ H × e × p × t, where H is the attacker’s hashrate, e is energy consumed per unit of hashing, p is the energy price and t is attack duration. That is only the operating layer. A realistic estimate must add hardware acquisition or rental, cooling, facilities, displaced honest-mining revenue, financing and the possibility that the attacked asset loses value.
The formula is useful not because it gives a precise dollar number for a “51% attack,” but because it shows that PoW imposes a recurring external cost. An attacker does not merely acquire influence once. Sustaining the attack requires continuing to compete with the honest network’s flow of work.
Capital cost and irreversible loss are not the same thing
Mining hardware does not necessarily disappear after an attack. ASICs may continue operating, be resold or, in some cases, be redirected to another network using a compatible algorithm. That means the purchase price of equipment is not the same as the amount irreversibly burned by the attack.
This distinction matters in every security model. The meaningful question is not “how many assets did the attacker control?” but “how much value could not be recovered after the attack?” PoW often imposes a significant operating burn through energy and opportunity cost, while leaving some residual hardware value.
Proof of Stake: consensus influence is tied to capital inside the protocol
In a PoS network, validators lock or commit an asset and receive a protocol-defined role in proposing blocks, attesting, voting or committing. There is no global ASIC race for each block. Instead, the protocol maps stake into voting power and makes certain kinds of contradictory behavior cryptographically provable.
Ethereum is a useful concrete example. Validators participate in fork choice and checkpoint voting, while Casper FFG provides a finality mechanism. This is more structured than the phrase “the richest validator writes the block.” A validator signs specific messages in specific slots and epochs. If those signatures contradict one another in slashable ways, the evidence can be shown to the protocol.
Slashing: turning stake into a potentially disposable attack weapon
Slashing is not simply a punishment for an Ethereum validator being offline. Ordinary non-participation is handled through missed rewards and other penalties. Slashing targets specific provable conflicting actions, such as proposing two blocks for the same slot or signing contradictory attestations.
That changes the attack economics. A PoW attacker pays for external resources, but the network does not automatically destroy the attacker’s ASICs. A PoS protocol can directly destroy some stake associated with provably unsafe behavior. Correlated violations can also be penalized more severely than a single isolated validator mistake, which is important because a coordinated attack should not look economically equivalent to one operator’s accidental error.
PoS thresholds are protocol-specific
Ethereum documentation describes different capabilities as the attacker’s share of active stake grows. Roughly one-third can interfere with finality, while larger shares unlock additional ways to influence consensus. Those numbers are properties of Ethereum’s specific fork-choice and finality design. They are not universal constants for every PoS chain.
A different BFT-style network can have a different validator set, quorum, commit rule and recovery procedure. So the sentence “33% is enough to attack PoS” is nearly meaningless without the protocol name and attack objective. Thirty-three percent of what: active stake, voting stake, committee power? Does the attacker gain finality delay, censorship, conflicting finality or a reorganization? Which actions are slashable? Security analysis needs those details.
Energy versus capital is a bad binary frame
The most common PoW-versus-PoS comparison is energy use. PoS consensus production does not require a continuous global computation race equivalent to Bitcoin mining. But it does not follow that PoS security is free. It depends on locked capital, validator infrastructure, operational discipline, software diversity and the protocol’s ability to enforce penalties.
Likewise, high PoW energy use is not automatically proof of high security. If hashrate is operationally concentrated, if specialized equipment is controlled by a small set of entities, or if power infrastructure creates a shared geographic failure domain, aggregate energy consumption does not describe the entire threat model. Distribution of control matters as much as total resource volume.
Hashrate can be rented and capital can be borrowed, but the markets are not symmetric
In theory an attacker can rent hashrate or borrow capital. In practice the liquidity of those resources is very different. A huge quantity of ASIC capacity cannot necessarily be rented instantly without affecting prices, availability or logistics. Likewise, acquiring a large share of a liquid token and converting it into active validator power can be slowed by market impact, activation queues, staking mechanics, custody constraints or simply the visibility of the operation.
This is why market capitalization is not the cost of a PoS attack, and the replacement value of every miner is not the cost of a PoW attack. What matters is the resource that is technically and economically available to the attacker during the required window.
What happens after a successful attack
After a serious PoW reorganization, nodes still apply validity rules. Exchanges can increase confirmation requirements or pause deposits and withdrawals. Miners can lose future revenue if trust in the asset collapses. Developers and infrastructure operators may coordinate emergency changes. The social and operational layer does not disappear just because the protocol uses physical work.
PoS makes this social layer particularly explicit in extreme scenarios. Ethereum documentation discusses community coordination as a final line of defense in some attacks involving finalized history. That is not evidence that PoS alone has a “human backdoor.” Every production network has people, clients, operators and applications that decide what to do after catastrophic failure. The relevant distinction is how clearly the protocol defines automatic recovery before social recovery becomes necessary.
Finality changes the question from “who builds faster?” to “what can no longer be reverted normally?”
In classical PoW reasoning, confidence typically grows with block depth. The more work is built above a transaction, the more expensive it becomes to catch up and replace that branch. This is probabilistic finality, and applications choose confirmation thresholds according to risk.
Ethereum PoS has an explicit checkpoint-finality mechanism. Once the required validator votes are collected, a checkpoint can become finalized. This gives applications a different kind of signal: not merely “there are N blocks above this transaction,” but “the consensus layer has finalized the relevant checkpoint.” That stronger term still rests on assumptions about honest stake, client correctness and network conditions.
Censorship, double spending and invalid rule changes are different attacks
Discussions often collapse every threat into a “51% attack.” In reality an attacker may want very different capabilities. Censorship means excluding or delaying selected transactions. A double spend requires an alternative history in which the attacker’s own earlier payment is absent or replaced. A finality-delay attack tries to prevent the required quorum from forming. Creating coins outside issuance rules or spending someone else’s balance without a signature is a validity attack and is normally rejected independently by full nodes.
This distinction is essential. Control over block production does not grant ownership of private keys. Consensus orders valid state transitions; it does not erase cryptographic authorization rules. Every attack analysis should begin by naming the property at risk: safety, liveness, censorship resistance, ordering or settlement finality.
Concentration: mining pools and staking providers complicate the map of control
PoW can look decentralized if we count ASIC owners, while block production is coordinated through a relatively small set of mining pools. Pool share is useful, but it is not identical to hardware ownership because miners can change pools. A pool’s visible block share therefore measures coordination power more directly than ultimate economic ownership.
PoS has a comparable distinction among token holders, validators, staking providers, liquid staking protocols and custodians. One economic owner can delegate to another technical operator. Thousands of validator indices can still depend on the same client stack, custody system or organizational decision maker. Counting validators without mapping control relationships can hide meaningful concentration.
Client diversity and software risk
Consensus is implemented in software. A critical bug shared by a dominant client can create a chain split or incorrect behavior even when the economic resource distribution looks healthy. Security budgets therefore include implementation quality, test coverage, client diversity, upgrade discipline and incident response.
This applies to both models. PoS clients must correctly process attestations, fork choice and finality. PoW clients still define which blocks are valid and which chain satisfies the protocol rules. Economics can discourage malicious behavior; it cannot compensate for every consensus-critical software bug.
A comparison matrix without declaring a winner
At a high level, PoW forces an attacker to keep funding external computational resources and compete continuously with honest work. PoS forces an attacker to control a significant share of internal capital and, in slashable scenarios, risk having that capital destroyed. PoW resource levels are easy to observe as hashrate but difficult to convert into a precise attack price. PoS influence is easy to express as a fraction of stake, but the cost of acquiring, activating and risking that stake is equally difficult to reduce to one number.
PoW anchors security in the physical world. PoS anchors it more directly in protocol-native capital. PoW attackers may retain residual hardware value but continue paying operating costs. PoS attackers avoid the computation race but can face direct capital destruction. PoW usually accumulates reorg resistance gradually; PoS systems can provide explicit finality checkpoints. None of those facts makes one model universally superior. The answer depends on what the network is trying to optimize and which assumptions are acceptable.
A practical checklist for evaluating consensus security
First, identify the resource that creates consensus influence: hashrate, active stake, validator power or committee votes. Second, find the fork-choice rule. Third, separate transaction validity from canonical-history selection. Fourth, find the exact definition of finality. Fifth, identify which violations are cryptographically provable and which penalties are enforceable.
Sixth, measure concentration across owners, operators, pools, custodians and software clients rather than relying on one chart. Seventh, ask what an attacker can do with 10%, 30%, 50% and larger shares in this specific protocol. Eighth, inspect the recovery path after a critical incident. Ninth, study whether attack resources can be rented or acquired quickly. Tenth, distinguish temporarily controlled capital from irreversible attack loss.
The main conclusion
Proof of Work and Proof of Stake are not two political identities. They are engineering systems that make different resources scarce and convert consensus violations into different forms of economic pain. PoW makes history rewriting compete against a continuing stream of computational work. PoS makes consensus influence depend on validator capital and can place that capital directly at risk when provable safety violations occur.
So the question “which is safer, PoW or PoS?” has little meaning without the network name, resource concentration, fork-choice rule, finality model, client diversity and attack objective. A better question is: which resource protects the property we care about, how accessible is that resource to an attacker, how much of it becomes irrecoverably lost, and how does the system recover if the economic defense still fails?
FAQ
Can 51% hashrate steal someone else’s bitcoin? No. Majority hashrate can influence ordering, censorship and reorganizations within consensus rules, but it cannot create the private-key signature required to spend another user’s coins or make an otherwise invalid transaction valid.
Is slashing just a penalty for an Ethereum validator going offline? No. Ordinary downtime and slashing are different. Slashing applies to specific provable conflicting messages, while inactivity is handled through missed rewards and other penalties.
Why is market capitalization not the cost of a PoS attack? An attacker needs stake that can actually be acquired, activated and used in consensus. Buying that stake changes the market price, liquidity can be limited, activation can take time, and slashable attacks can destroy part of the capital.
Why is network hashrate not a dollar price for a PoW attack? Hashrate measures computation. Dollar cost depends on ASIC efficiency, electricity prices, available hardware, cooling, facilities, duration, financing and residual hardware value.
Does PoS have a universal 51% attack threshold? No. Exact thresholds and effects are protocol-specific. Ethereum, for example, assigns different capabilities to different shares of stake. The same percentages should not be copied to unrelated PoS networks.
Why does finality matter more than block time for settlement risk? Fast block production only tells you how often new candidates appear. Finality describes when ordinary protocol operation should no longer replace the relevant history, which is the property an application needs for irreversible settlement.
This material is educational and informational. It is not financial advice or a trading signal.